Secure Solution for Rotterdam Port
Note: This was a hypothetical class project set by Fontys, not real client work for Rotterdam Port, we didn't work directly with the port's organization.
Background
My group worked on a defensive cybersecurity project modeled on a real ransomware attack that hit Rotterdam Port and affected several other entities, including an APM container terminal, an MSD pharmaceutical site, and a TNT package carrier. The attack paralyzed operations across these organizations, which is what motivated the exercise: design a secure infrastructure that could realistically have prevented it.
Client Requirements
The (simulated) client meeting outlined the goal clearly: build a resilient, proactive cybersecurity infrastructure to mitigate the risk of a repeat incident. One detail from the brief stuck with the team, the original infrastructure had no network segmentation, which was a major reason the ransomware spread as fast as it did.
Secure Solution Design
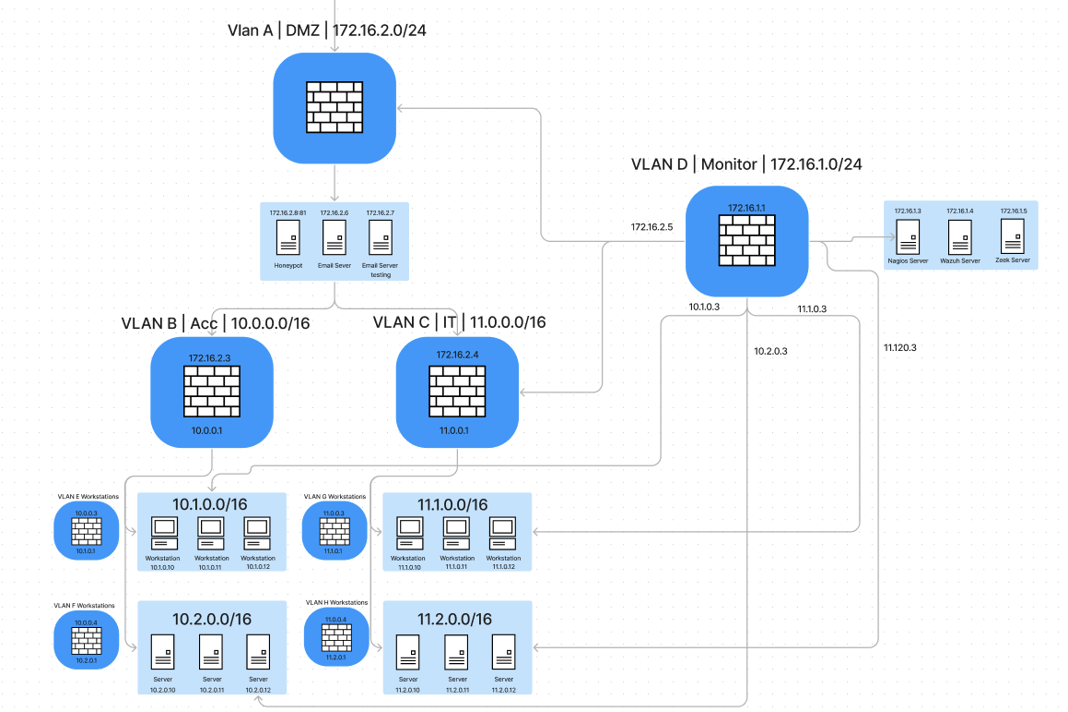
The proposed solution had three main pillars:
1. Network segmentation. Eight VLANs, each behind a pfSense firewall running Suricata with tuned Snort rules to detect malicious activity, directly addressing the segmentation gap that let the original attack spread unchecked.
2. Email security. A dedicated email server built around Phishtool for analyzing and reverse-engineering suspicious emails, plus employee training material on spotting malicious email, since the real-world attack's root cause was a phishing email.
3. Monitoring infrastructure.
- Nagios XI, infrastructure-wide anomaly monitoring.
- Wazuh, host-level agents on every machine, taking automated action against suspicious files.
- Zeek, network-layer monitoring across all devices.
- Honeypot, placed in the DMZ to draw out and observe malicious activity.
Implementation
The team started with a full network diagram (IP addressing, firewall structure, monitoring tool placement) validated against the client's requirements, then implemented it with consistent machine naming and IP conventions throughout.
Reflection
Simulating a real client engagement, from requirements gathering through to a segmented, monitored architecture, was both enjoyable and genuinely instructive. It gave the team a much clearer picture of how the individual tools (pfSense, Suricata, Wazuh, Nagios, Zeek) fit together into one coherent defensive posture, and reinforced just how much a single missing control (network segmentation, in the real incident) can undermine everything else.